Ahead of the Mandate: How NIST's Emerging Acoustic Authentication Standards Are Forcing Enterprise Security Into Uncharted Territory
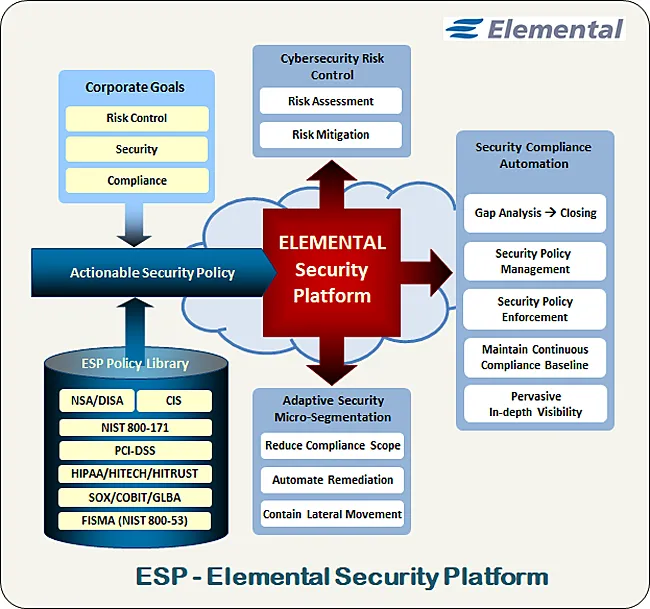
Photo: enterprise security compliance meeting government standards technology, via www.elementalsecurity.com
The Standards Are Moving. Most Enterprises Are Not.
For years, acoustic authentication existed in a regulatory gray zone — acknowledged informally by security practitioners, yet largely absent from the codified frameworks that govern enterprise compliance. That era is ending. NIST's ongoing revision cycles, particularly work emerging from its Digital Identity Guidelines and broader cybersecurity framework updates, are beginning to incorporate explicit language around voice-based authentication mechanisms, acoustic threat vectors, and the environmental conditions under which biometric credentials can be considered reliable.
The implications for enterprise security teams are significant. Organizations that have operated under the assumption that password policy compliance and MFA deployment represent the ceiling of authentication governance are now confronting a more demanding reality. Acoustic authentication — both as a security capability and as a vulnerability category — is entering the regulatory mainstream, and the window to prepare proactively rather than reactively is narrowing.
What the Emerging Framework Actually Requires
NIST's guidance does not move in sudden leaps. It evolves through public comment periods, internal working group deliberations, and iterative publication cycles that can span years. But the directional signal embedded in recent drafts is unmistakable. The updated Digital Identity Guidelines, for instance, are increasingly attentive to the conditions under which biometric authentication — including voice — can meet the threshold for Authenticator Assurance Level 2 and Level 3 designations.
This matters because AAL classifications directly influence what authentication methods are considered acceptable for high-sensitivity access scenarios. Under the emerging framework, enterprises seeking to deploy voice biometrics at higher assurance levels must demonstrate not only that the technology functions accurately, but that the acoustic environment in which it operates is sufficiently controlled to prevent spoofing, replay attacks, and synthetic voice injection.
In practical terms, this means compliance will require documentation of acoustic security controls that most organizations have never formally inventoried. It means demonstrating that voice authentication systems are tested against adversarial conditions — not merely evaluated for accuracy under ideal circumstances. And it means establishing audit trails that regulators can examine to verify that acoustic authentication infrastructure meets the same evidentiary standards applied to other credential categories.
Fortune 500 Organizations Are Already Recalibrating
Inside the security organizations of large financial institutions, healthcare conglomerates, and defense contractors, the conversation has shifted from whether to prepare for acoustic authentication compliance to how quickly it can be operationalized. Several major banks operating under OCC oversight have begun internal gap assessments specifically focused on voice channel security, driven in part by NIST's evolving language and in part by parallel guidance from the CFPB around remote authentication in consumer-facing financial services.
Healthcare systems navigating the intersection of HIPAA and emerging NIST standards face a particularly acute challenge. Voice-based authentication is increasingly embedded in clinical workflows — from physician access to electronic health records to nurse station authentication in high-traffic environments. The acoustic conditions in those environments are rarely controlled, and the NIST framework's emerging emphasis on environmental verification creates a compliance burden that many health system CISOs acknowledge they are not currently equipped to meet.
In the defense industrial base, where CMMC compliance already demands rigorous authentication controls, contractors are watching NIST's acoustic guidance with particular attention. The overlap between CMMC Level 2 and 3 requirements and NIST SP 800-63 revisions means that organizations already managing one compliance framework will soon need to reconcile it with standards that treat acoustic attack surfaces as first-class security concerns.
The Gap Between Awareness and Readiness
One of the more striking findings from enterprise security assessments conducted across multiple sectors is the divergence between awareness and operational readiness. Security leaders are increasingly familiar with acoustic authentication as a concept. They understand, at least in principle, that voice biometrics introduce attack surfaces that conventional authentication frameworks do not address. But awareness has not translated into the infrastructure investments, policy updates, and workforce training programs that compliance will ultimately require.
Part of the challenge is organizational. Acoustic authentication spans multiple domains — physical security, IT infrastructure, compliance, and end-user experience — and in most enterprises, those domains report to different stakeholders with different budget cycles and different definitions of success. Coordinating a compliance response across that landscape requires a level of cross-functional alignment that many organizations have not yet established.
Part of the challenge is also technical. Legacy authentication infrastructure was not designed with acoustic security controls in mind. Retrofitting those systems to meet emerging NIST standards is not simply a matter of software updates. It may require environmental assessments of physical spaces where voice authentication occurs, hardware upgrades to capture devices, and integration work that touches identity management platforms, SIEM systems, and access control infrastructure simultaneously.
Proactive Compliance as Competitive Positioning
Organizations that move ahead of the mandate rather than scrambling to meet it will be positioned to capture measurable advantages. For enterprises operating in regulated industries, the ability to demonstrate acoustic authentication compliance before it becomes mandatory signals a level of security maturity that influences enterprise procurement decisions, insurance underwriting, and regulatory relationship quality. Auditors notice when organizations have anticipated standards rather than reacted to them.
There is also a practical operational benefit to early adoption. Enterprises that begin acoustic authentication compliance work now — conducting environmental assessments, updating identity governance policies, and piloting NIST-aligned voice authentication controls — will have the organizational muscle memory and documented evidence trails that make formal audits significantly less disruptive when compliance deadlines arrive.
The Mandate Is Not Here Yet. The Preparation Window Is.
NIST's acoustic authentication guidance has not yet crystallized into hard compliance mandates with enforcement teeth. But the trajectory is clear, and the history of enterprise security regulation offers a consistent lesson: organizations that treat emerging standards as distant concerns consistently find themselves under-resourced and overexposed when those standards arrive with urgency.
The enterprises that will navigate this regulatory shift most effectively are the ones investing now in understanding exactly where their acoustic authentication posture falls short, which systems require modernization, and what a credible compliance roadmap looks like across their specific operating environment. The reckoning is coming. The question is whether your organization will meet it prepared or reactive.