What Security Audits Are Not Hearing: The Acoustic Attack Surface CISOs Cannot Afford to Ignore
Photo: CISO security audit meeting enterprise boardroom technology, via securitybrief.co.uk
The Audit That Passes While the Threat Persists
Every year, enterprise security teams invest significant resources in penetration testing, compliance reviews, and authentication audits. Frameworks such as SOC 2, ISO 27001, and NIST SP 800-63 provide structured guidance for evaluating identity and access management controls. Yet a growing category of threat actor—one exploiting acoustic and voice-based attack surfaces—continues to operate largely beneath the radar of these established methodologies.
The result is a troubling paradox: organizations that achieve full marks on a security audit may still be deeply exposed. For CISOs navigating this landscape, the challenge is not simply technical. It is structural. The audit frameworks themselves were not designed with acoustic attack vectors in mind, and updating institutional practices to account for them requires both awareness and deliberate effort.
Why Conventional Frameworks Fall Short
Standard authentication audits tend to concentrate on a familiar set of control categories: password policies, multi-factor authentication configurations, session management, and credential storage practices. These are legitimate and necessary areas of scrutiny. However, they share a common blind spot: they evaluate authentication systems as discrete digital constructs, divorced from the physical and acoustic environments in which those systems actually operate.
Consider a typical enterprise scenario. A voice-enabled authentication system may pass every technical control assessment—encryption in transit, secure token handling, compliant API design—while remaining entirely vulnerable to replay attacks using recorded voice samples, adversarial audio injections, or ambient sound harvesting conducted within open-plan office environments. None of these attack vectors require compromising a server. None of them trigger a firewall alert. And none of them appear on a standard penetration testing checklist.
The gap is not a failure of individual auditors. It reflects a systemic absence of acoustic security competency within the frameworks themselves. Most penetration testers are not trained in acoustic signal analysis. Most compliance checklists do not include questions about microphone access controls, speaker verification degradation thresholds, or the physical propagation characteristics of sensitive audio in shared workspaces.
The Attack Surface Auditors Are Not Measuring
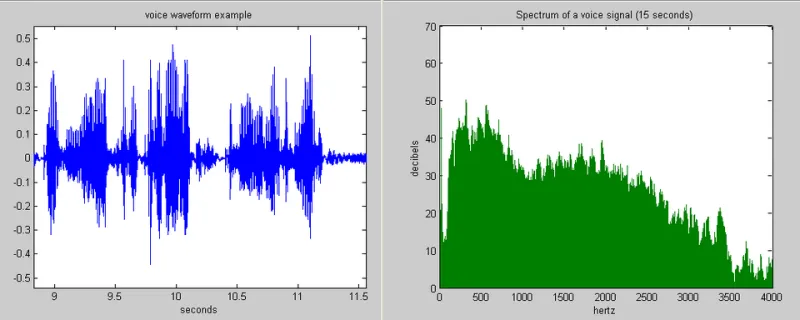
To understand what is being missed, it helps to map the acoustic attack surface explicitly. Authentication systems that incorporate voice biometrics, ambient noise analysis, or sound-based device fingerprinting introduce a set of vulnerabilities that are genuinely distinct from their digital counterparts.
Replay and synthesis attacks represent perhaps the most widely documented acoustic threat. Sophisticated voice cloning tools—several of which are now commercially available and require only a few seconds of source audio—can generate synthetic speech that defeats voice authentication systems not equipped with liveness detection. Standard audits rarely test whether a voice authentication implementation can distinguish a live speaker from a high-fidelity synthetic reproduction.
Acoustic eavesdropping poses a separate but related risk. In environments where authentication challenges are delivered via speaker or where users verbalize credentials, ambient audio capture becomes a viable attack pathway. This is particularly relevant in shared workspaces, open-plan offices, and hybrid work environments where physical acoustic boundaries are inconsistent or absent.
Side-channel acoustic attacks are a more sophisticated category, involving the analysis of environmental sounds—keyboard acoustics, device vibrations, HVAC interference—to infer credential input or user behavior. While these techniques require greater attacker sophistication, their very obscurity means they are almost never assessed during a standard engagement.
A Framework for Acoustic-Aware Authentication Audits
Addressing these gaps requires CISOs to extend their audit frameworks along several dimensions. The following areas represent a practical starting point for organizations seeking to evaluate their authentication posture through an acoustic lens.
Liveness detection assessment. Any voice authentication deployment should be tested against both recorded and synthetically generated audio samples. Auditors should verify that liveness detection mechanisms meet current standards and are updated in response to advances in voice synthesis technology. This is not a one-time evaluation; it requires periodic reassessment as the threat landscape evolves.
Physical environment review. Authentication workflows should be mapped against the physical spaces in which they are used. Areas where voice-based authentication is common—call centers, executive offices, shared conference rooms—should be evaluated for acoustic containment. This includes reviewing microphone placement, ambient noise levels, and proximity to untrusted individuals or recording-capable devices.
Access controls for audio hardware. Endpoint policies governing microphone access are frequently underspecified. Auditors should verify that microphone permissions are governed by least-privilege principles, that access logs are maintained, and that unauthorized audio capture attempts generate alerts within the SIEM environment.
Vendor questionnaires with acoustic specificity. Third-party authentication providers should be asked directly about their acoustic security posture. What liveness detection mechanisms are in place? How frequently are voice models updated? What is the vendor's policy for disclosing vulnerabilities related to synthetic audio attacks? Many vendor assessments currently omit these questions entirely.
Red team scenarios incorporating acoustic vectors. Penetration testing engagements should include acoustic attack simulations where voice authentication is in scope. This may require engaging specialists with relevant signal processing expertise, but the investment is proportionate to the risk.
The Organizational Dimension
Beyond technical controls, CISOs should consider the organizational factors that perpetuate acoustic blind spots. Security awareness training rarely addresses voice-based social engineering or the risks of verbalizing credentials in shared environments. Physical security teams and IT security teams frequently operate in separate silos, meaning that acoustic risks with both physical and digital dimensions fall between organizational responsibilities.
Closing these gaps requires deliberate cross-functional coordination. Physical security leadership should be included in authentication audit planning. Facilities teams should be consulted when evaluating acoustic containment in spaces where sensitive authentication workflows occur. And procurement teams should be equipped with acoustic security criteria when evaluating new identity solutions.
Raising the Standard
The authentication audit has long been a cornerstone of enterprise security governance. As authentication systems increasingly incorporate acoustic and voice-based modalities, the audit must evolve accordingly. The organizations that will be best positioned to manage emerging acoustic threats are those that begin expanding their evaluation frameworks now—before a breach makes the gap impossible to ignore.
For CISOs, the imperative is clear. Passing an audit is not the same as being secure. The acoustic attack surface is real, it is growing, and it is not yet reflected in the frameworks most enterprises rely upon. Addressing that discrepancy is not an optional enhancement. It is a foundational security responsibility.